Store Less, Survive More: Why Data Minimization Protects Agents From Personal Liability
The data you don't hold can't be stolen, subpoenaed, or the basis of a missed notification. Data minimization is the only control that cuts both breach risk and liability.
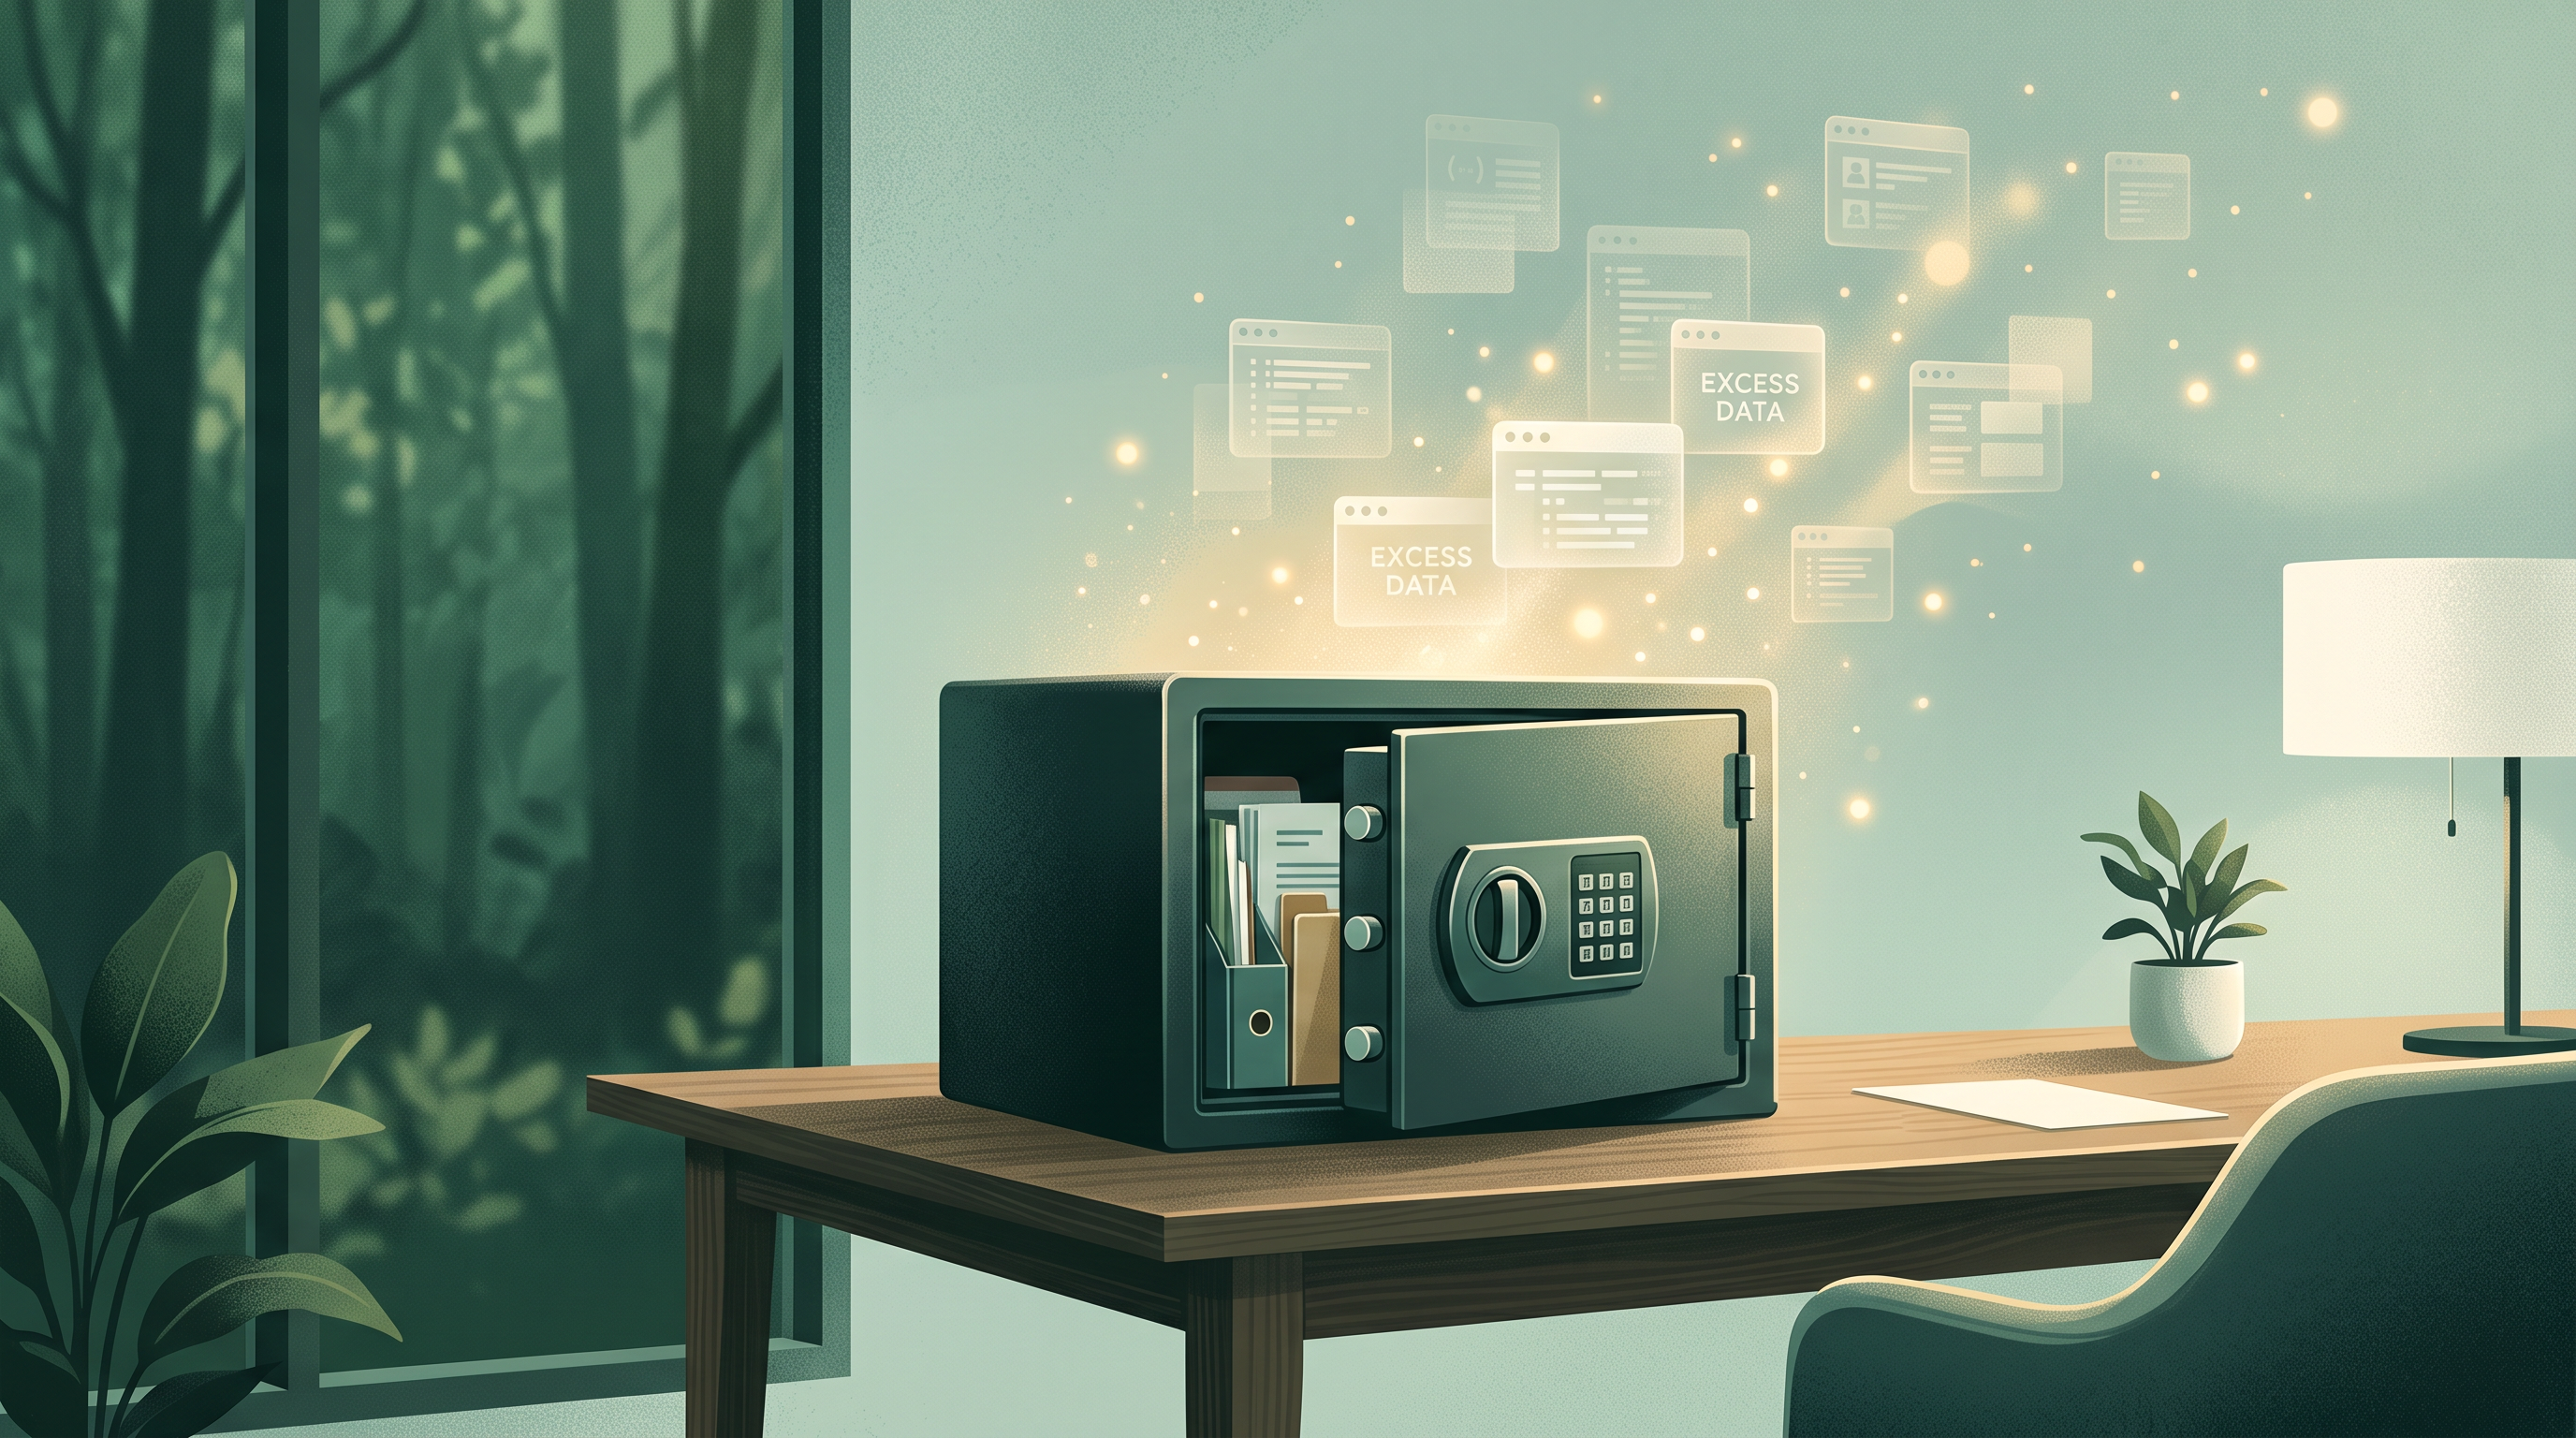
The cheapest cybersecurity control an agency can deploy is also the one most agencies never implement: storing less data. Data minimization — collecting and retaining only the personal information you actually need to place a policy — is now a written requirement under state privacy laws and a practical defense against the personal liability that increasingly follows insurance owners and producers when consumer data is mishandled.
Most agencies store far more than they need. A lead list purchased three years ago, a spreadsheet of prospects who never bought, a CSV of client health questions exported "just in case" — each one is a liability you keep paying to carry. Every unnecessary record is a record you must encrypt, log, segment, and eventually notify consumers about if it is breached.
How Data Minimization Reduces Personal Liability
The liability that reaches an individual agent or agency owner is no longer hypothetical. State privacy statutes like the CCPA (as amended by the CPRA), the Colorado Privacy Act, and the Connecticut Data Privacy Act create private rights of action and regulatory enforcement that can attach to the individuals who made the storage decisions, not just the corporate entity. When an agency can show it never stored the data at issue — because it followed a documented minimization policy — that data simply cannot be the basis of a claim.
The principle is simple: the data you don't hold cannot be stolen, cannot be subpoenaed, and cannot be the subject of a notification you fail to send. Our onboarding and data migration process is built around retention-by-design, so that agencies arriving on Kaffeine start with a clean inventory rather than inheriting a decade of unnecessary exposure.
What a Minimization Policy Actually Looks Like
A working data-minimization policy for an insurance agency has three parts:
- Collection limits — capture only the fields required to quote and place a policy. Drop the "nice to have" PII that lives in a notes field.
- Retention limits — define how long each category of data lives. Expire stale leads automatically; archive closed policies on a schedule rather than keeping them live forever.
- Disposal — actually delete. A record marked "deleted" that still sits in an export folder is not deleted; it is a liability in waiting.
A HIPAA-compliant CRM with structured retention controls makes all three enforceable from the platform rather than dependent on producer discipline. Our pricing reflects the fact that minimization tooling is a baseline control, not a premium add-on.
The Compliance Reality
Under the GLBA Safeguards Rule — which applies to insurance entities as financial institutions — and the NAIC Data Security Model Law, licensees are expected to maintain an information security program that includes data retention and disposal. A program that lets producers keep unlimited local copies of client data in personal files is not a program; it is a liability ledger. Our security framework was designed to keep client data inside the controlled environment, where minimization and disposal are real, not aspirational.
The Takeaway
The agency that survives the next wave of privacy enforcement will not be the one with the biggest firewall. It will be the one that stored the least, retained it for the shortest defensible period, and could prove it deleted what it no longer needed. Data minimization is the only security control that reduces both your breach probability and your liability at the same time.
— G. David Humphries, Kaffeine Security